Bank-Grade Security, Certified Compliance & Uncompromising Trust
At KIVO, protecting your data, operations, and intellectual property is not an afterthought; it is our foundation. We operate under formal ISO 27001 certification, 100% on-site institutional facilities, and a strict Clean Desk Policy.
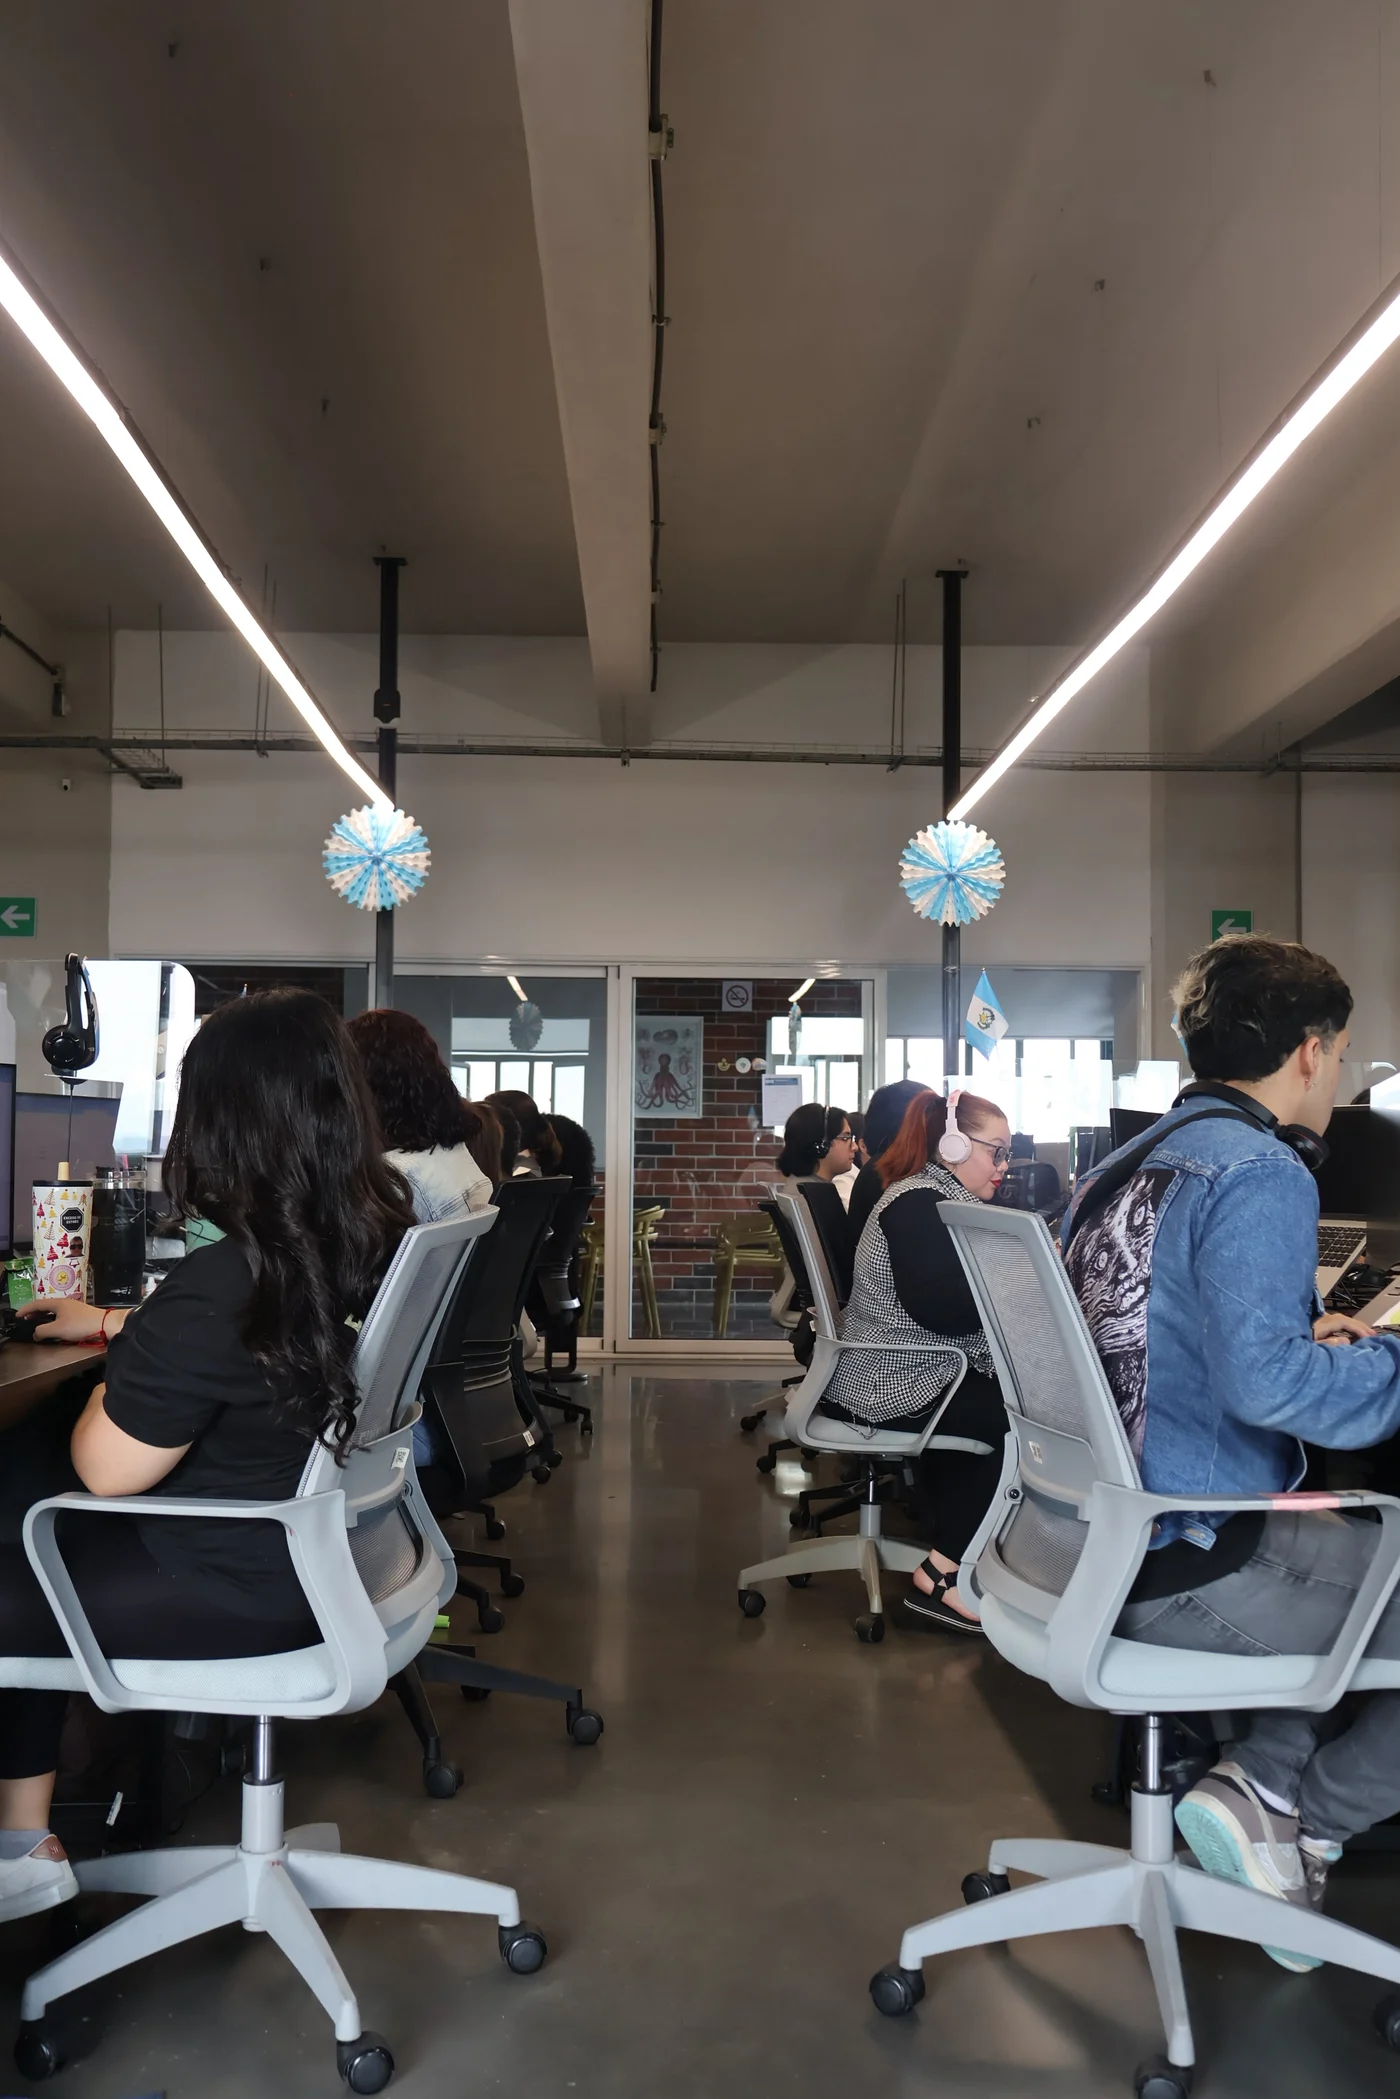
Campus Tec III • Guatemala City
Center of Excellence & ISO 27001 Compliance
What Does Our ISO/IEC 27001:2022 Certification Mean for Your Business?
ISO/IEC 27001 is the world’s most prestigious benchmark for information security management systems (ISMS). It verifies that KIVO has engineered, implemented, and continuously maintains robust security protocols audited by accredited third parties to eliminate operational risks.
Independent Third-Party Audits
Our controls and security workflows are tested and audited annually by accredited external registrars.
Active Risk Management
Proactive identification, assessment, and remediation of physical, network, and human risk vectors.
Segregated Partner VLANs
Zero network crossover. Dedicated VLANs ensure partners operate in strictly isolated broadcast environments.
Biometric Physical Security
Facial and fingerprint checkpoints, 24/7 CCTV surveillance, and enforceable clean-desk operational bays.
The 4 Core Security Pillars of KIVO
We combine world-class physical facilities, advanced cyber defense, and strict talent governance.
1. Physical Security & Clean Desk Policy (Campus Tec III)
Unlike vendors relying on scattered work-from-home contractors with unsecured WiFi and home distractions, KIVO is 100% on-site at Campus Tec III, Central America’s premier tech district.
- Facial and fingerprint biometric turnstile access.
- 24/7 CCTV surveillance across entries and operation floors.
- Enforced Clean Desk: no personal phones, cameras, or paper notes.
- Corporate terminals with physically/digitally disabled USB ports.
2. Network Defense & Client Isolation
We enforce a Zero-Trust network architecture to guarantee each partner’s environment remains strictly segregated and impenetrable.
- Dedicated VLANs with Layer 2/3 isolation per client.
- Enterprise Fortinet/Cisco firewalls with active IPS/IDS.
- Encrypted IPsec / SSL VPN tunnels with TLS 1.3.
- EDR endpoint protection and centralized security event logging.
3. Talent Governance, Background Checks & NDAs
Technical safeguards are hollow without rigorous human integrity. We conduct exhaustive vetting before any team member sets foot in our operations center.
- Exhaustive background, criminal, and financial checks.
- Legally enforceable NDAs and full intellectual property assignment.
- Continuous security awareness training and phishing drills.
- Enforced Least Privilege access protocols for all roles.
4. Business Continuity & Operational Resilience
Mission-critical operations cannot afford downtime. We maintain fully tested Business Continuity Plans (BCP) and Disaster Recovery (DRP) protocols.
- Redundant multi-carrier fiber internet with automatic failover.
- Industrial UPS battery backups + dedicated diesel generator.
- Guaranteed 99.9% facility and power availability SLA.
- Rapid incident response protocols with documented drills.
International Compliance Alignment
Our processes meet and adapt to the rigorous compliance requirements demanded by U.S. and global enterprises.
ISO/IEC 27001:2022
Formally certified Information Security Management System covering all operations and tech stacks.
SOC 2 Type II Ready
Operational framework aligned with AICPA Trust Services Criteria for security and confidentiality.
GDPR & CCPA Compliant
Strict alignment with European and California frameworks governing confidential personal data handling.
HIPAA & PCI Ready
Segregated operational bays and protocols ready for healthcare support and payment handling.
Security & Trust: Clear Answers
Can our security team audit KIVO or send a Vendor Security Assessment questionnaire?
Absolutely. Over 90% of our enterprise partners conduct annual security reviews. We readily provide our comprehensive Security Packet, ISO 27001 certificate, network diagrams, and complete your internal vendor assessments.
Who owns the intellectual property and work generated by the dedicated team?
You own 100%. All KIVO agreements and employment contracts include irrevocable Work-for-Hire and IP assignment clauses. Every line of code, document, data point, and deliverable is exclusively yours.
How do you prevent a team member from sharing data across different partners?
Through physical and logical segregation. Dedicated teams operate in restricted floor bays on isolated VLANs with role-based credentials, supervised on-site by real-time Team Leads and QA managers.
Ready to Scale with an ISO 27001 Certified Partner?
Schedule a technical call with our compliance leadership or request our security packet for your enterprise audit team.